Browser Extensions Are the New Exfiltration Channel for AI Chats
Security teams are discovering that everyday browser extensions can read — and quietly ship out — everything employees type into AI assistants. The clipboard was never the problem; the DOM is.
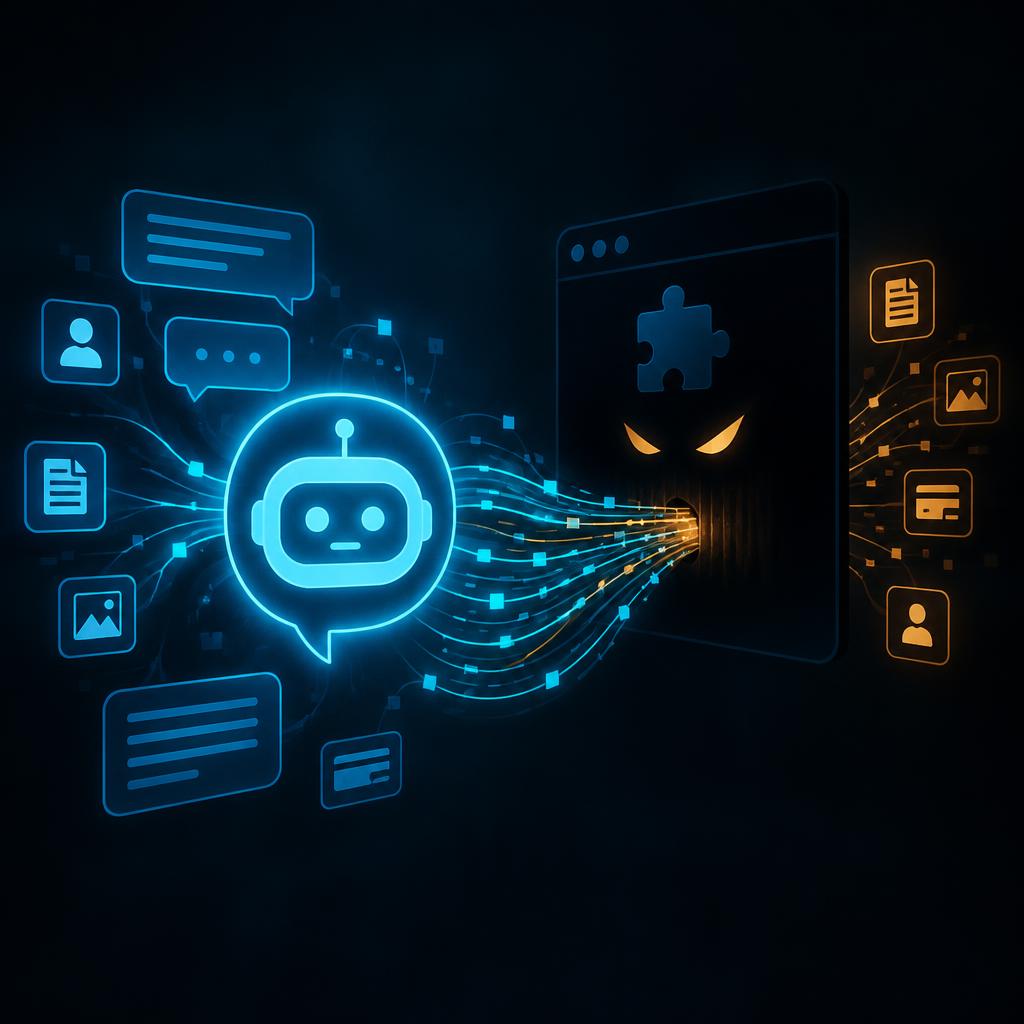
Enterprise security teams spent two years worrying about what employees paste into AI chatbots. The past quarter has made clear they were watching the wrong surface. The clipboard is visible, policy-controlled, and increasingly monitored. The browser DOM is none of those things — and it is where the actual leakage now happens.
Researchers tracking extension marketplaces have identified a growing class of add-ons that request broad 'read and change all your data on websites you visit' permissions, then quietly scrape the contents of AI chat sessions. The pattern is not new — coupon tools and grammar checkers have done versions of this for years — but the target has shifted. AI chat pages now contain the richest concentration of confidential text in the average knowledge worker's day: draft contracts, incident details, customer data, internal strategy.
Why DLP keeps missing it
Traditional data-loss-prevention tooling inspects network egress and clipboard events. A malicious or over-permissive extension operates inside the renderer process, below both. It reads the page after decryption and before any network proxy sees a thing. By the time the data moves, it is bundled into ordinary-looking analytics beacons to domains that pass reputation checks.
The economics favour the attacker. A popular extension with a hundred thousand installs is a pre-built collection pipeline. Acquisition of small extension developers — a long-standing grey market — has become a deliberate intelligence play: buy the distribution, push an update, inherit the permissions.
What actually works
- Maintain an explicit allowlist of extensions; block everything else by policy, not by request.
- Treat 'read all site data' as a privileged permission requiring security review, like local admin rights.
- Serve AI tools through isolated browser profiles or dedicated apps that exclude third-party extensions entirely.
- Monitor for sudden ownership changes and permission expansions in installed extensions — both are high-signal events.
The uncomfortable truth: most organisations have better inventory of their office chairs than of the code running inside their employees' browsers.
The deeper issue is architectural. Browsers were designed when the most sensitive thing on a page was a password field. Now the page *is* the workspace. Until extension permission models catch up, the safest assumption is that anything typed into a browser-based AI tool is readable by every extension in that profile.