The AI Coding Assistant Is Now Part of Your Supply Chain
Attackers have noticed that the fastest way into a thousand codebases is through the tools that write them. Poisoned suggestions, compromised extensions and typosquatted models are the new dependency confusion.
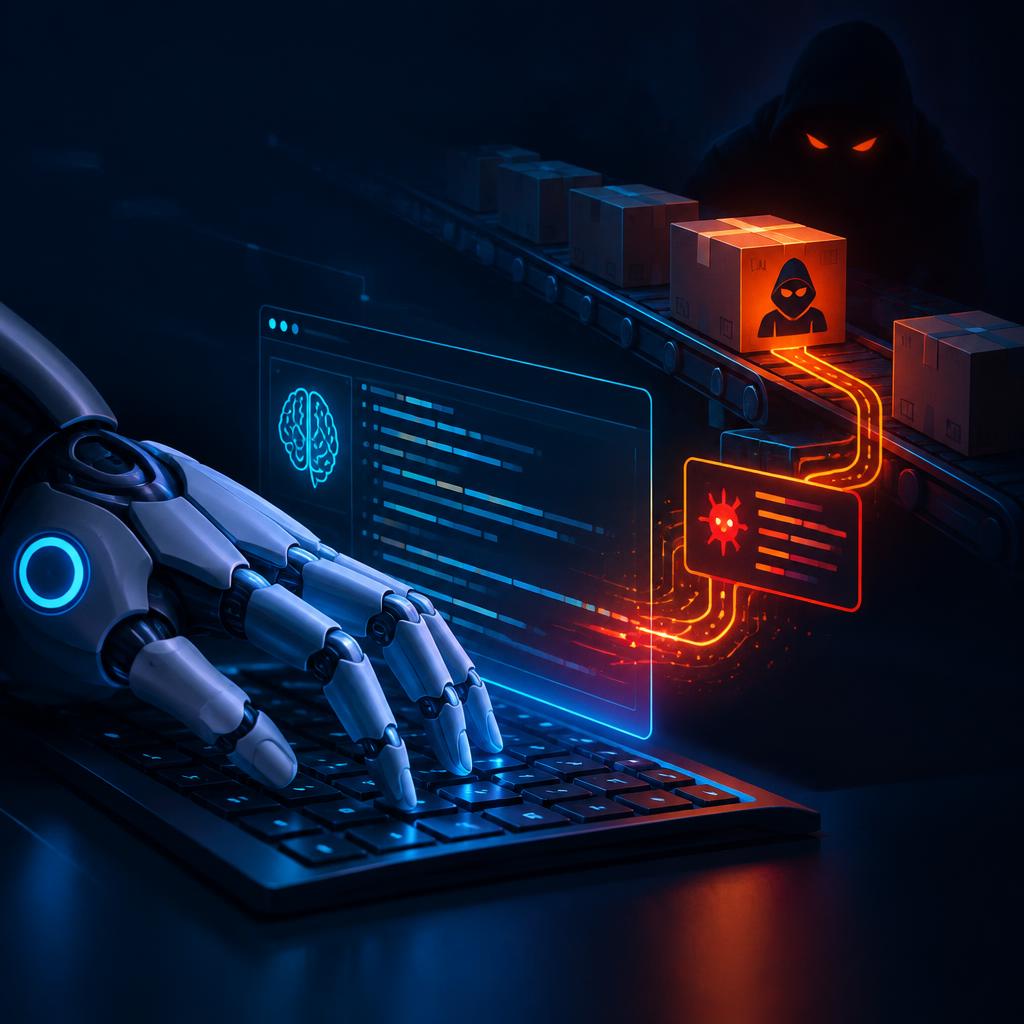
Dependency confusion taught the industry that developers will install almost anything that looks plausible. AI coding assistants have industrialised that insight: the suggestion arrives inline, looks idiomatic, and is accepted in a keystroke. Attackers have adapted accordingly.
The observed playbook has three moves. First, 'slopsquatting' — registering packages under names that models hallucinate, so that a confident suggestion of a non-existent library resolves to an attacker's package. Second, compromising the assistant's own toolchain: malicious IDE extensions that intercept or alter suggestions before they reach the editor. Third, poisoning the public code the models learn from, seeding patterns that encode vulnerable or exfiltrating idioms.
Why review processes miss it
Code review norms evolved for human authors. A reviewer reads for intent and logic; an AI-generated snippet has neither — it has plausibility. Subtle issues survive: a URL with one character changed, a serialisation call that quietly disables validation, a dependency pinned to a version with a known CVE. Each looks like a stylistic choice.
The volume problem compounds it. Teams using assistants report 30–50% more code per sprint. Review capacity did not grow 30–50%.
Controls that match the threat
- Pin and verify every suggested package against your registry allowlist before first install — automate this, do not ask developers to remember it.
- Treat IDE extensions as privileged software: inventory, version-pin and monitor them like production dependencies.
- Run SAST and secrets scanning on AI-generated code with the same rigour as vendor code, because that is what it is.
- Track acceptance rates of suggestions per developer; sudden shifts can indicate a compromised assistant configuration.
Your coding assistant has write access to every repository your developers touch. It is supply chain. Govern it like supply chain.
The vendors are responding — provenance metadata, suggestion signing, enterprise allowlists — but adoption lags. Until then, the pragmatic posture is simple: AI-generated code is third-party code written very quickly by an author you cannot fire.