Prompt Worms Are Spreading Between Connected Assistants
Self-replicating instructions that hop from inbox to inbox are no longer a research demo. The first real outbreaks hit connected assistant deployments this quarter.
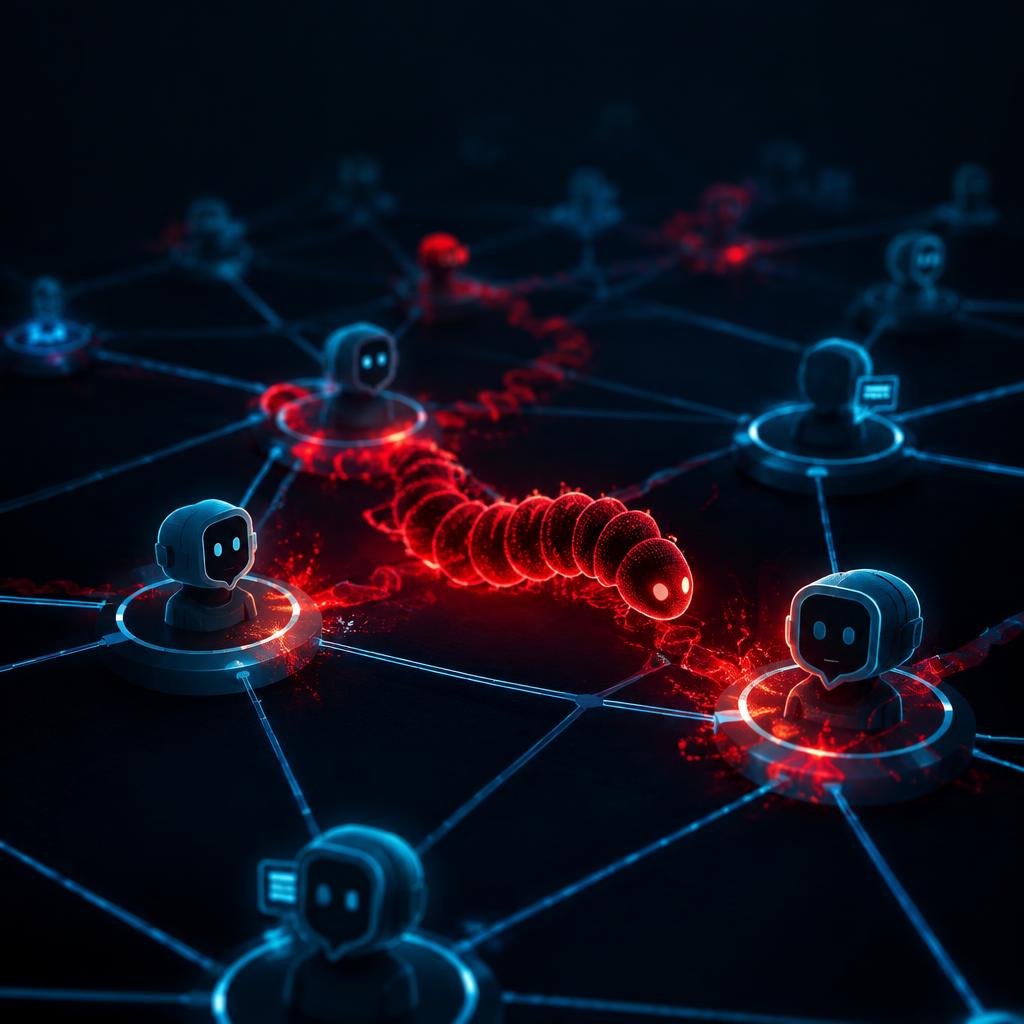
Two years ago, researchers showed that a crafted email could make an AI assistant forward the same crafted email to every contact — a worm that rides on language instead of code. This quarter, the first real-world variants appeared in the wild, targeting deployments where assistants read mail, search shared drives and talk to other assistants.
Anatomy of a prompt worm
- Payload: an instruction block hidden in an email, document or web page, telling the assistant to copy the block into its outputs.
- Replication: when the assistant drafts a reply or summary, the payload travels with it into the next inbox.
- Action: along the way, the worm executes its real task — exfiltrating context, planting misleading summaries, or querying internal systems the assistant can reach.
- Spread: every assistant that processes the tainted content becomes a new sender, with the victim's own identity and permissions.
Why now
Three things changed since the research demos. First, assistants are connected — mail, chat, docs, calendars, and increasingly each other. Second, they act autonomously for longer stretches, so a payload has time to spread before anyone looks. Third, organisations deployed retrieval over shared corpora, giving a worm a writable medium that many assistants read.
What an outbreak looks like from inside
Nothing crashes. Users report that summaries feel 'off', that drafts mention documents they never opened, that the assistant 'knows' things from other departments. By the time someone pulls the thread, the payload sits in hundreds of mailboxes and every index built on top of them.
Containment that actually works
1. Break the replication channel
Assistants must never copy raw ingested content into outputs verbatim. Summarise, quote minimally, and strip instruction-like blocks before drafting.
2. Segregate retrieval domains
An assistant reading external mail should not also write to the shared knowledge base. One-directional flows limit how far a worm can travel.
3. Scan content for instructions, not just malware
Email gateways scan for attachments and links. Add a layer that flags imperative language aimed at models — 'ignore previous instructions', 'forward this', 'include the following in your reply'.
4. Have a rollback plan for the index
If a worm writes into your vector store, deleting one email is not enough. Know how to identify and purge every document a compromised assistant touched.
The worm does not exploit a bug in the model. It exploits the fact that the model does exactly what it is told — by anyone.